
MoRTH Brings NHAI and NHIDCL Under Mandatory 282-Point Cybersecurity Framework with 6-Hour CERT-In Reporting
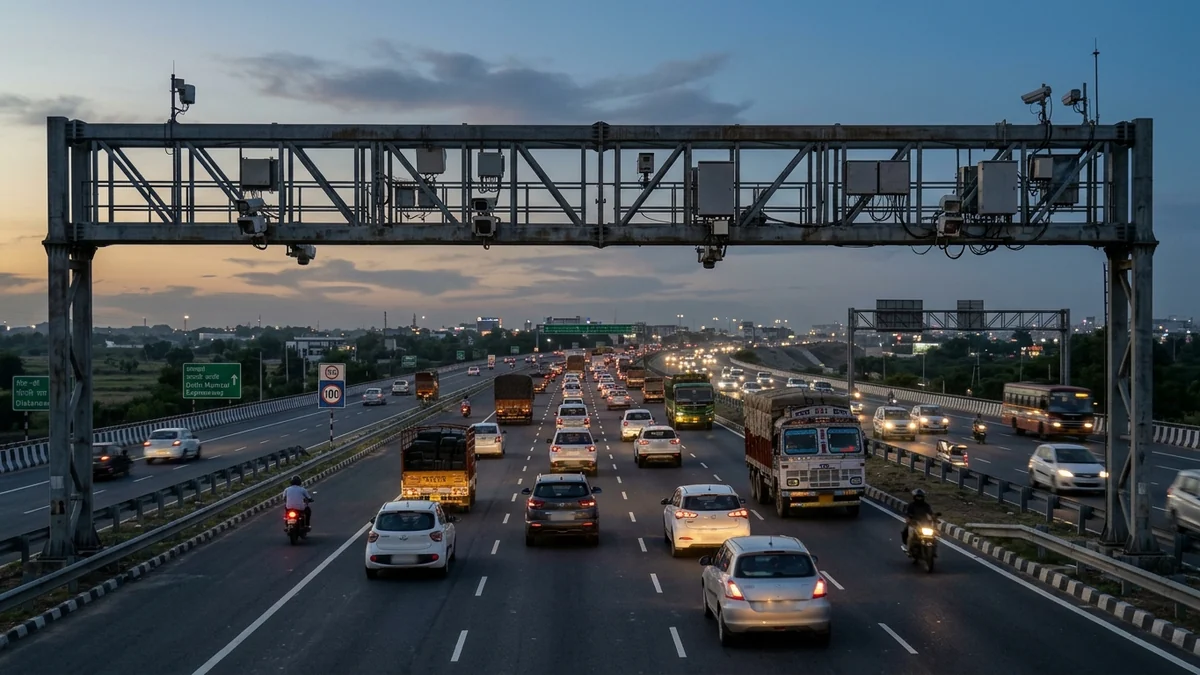
The Ministry of Road Transport and Highways (MoRTH) has placed the National Highways Authority of India (NHAI) and the National Highways and Infrastructure Development Corporation Limited (NHIDCL) under a binding cybersecurity compliance framework. Both national highway agencies must execute the security overhaul within a six-month implementation deadline, report cyber incidents to the Indian Computer Emergency Response Team (CERT-In) within six hours, and pass annual audits against a 282-point security checklist.
India's National Highway corridors now operate on tightly coupled digital infrastructure: electronic FASTag plazas, barrierless Multi-Lane Free Flow (MLFF) overhead gantries, Advanced Traffic Management System (ATMS) camera corridors, and real-time enforcement integrations with VAHAN and Parivahan servers. Protecting these connected highway systems against ransomware, toll-switch tampering, and data leaks prompted MoRTH's Information Technology section to enforce uniform national critical-infrastructure controls.
Core Mandates in the MoRTH Highway Cybersecurity Directive
Under the Ministry's directive—aligned with statutory cyber incident reporting powers under Section 70B of the Information Technology Act, 2000—NHAI and NHIDCL face five enforceable technical benchmarks:
| Compliance Pillar | Mandatory Standard / Timeline | Operational Scope Across Highway Assets |
|---|---|---|
| Full Framework Rollout | 6 Months from directive issue | Appointment of dedicated Nodal Security Officers; MoRTH IT Section oversight across NHAI & NHIDCL |
| Digital Asset Inventory Portal | 3 Months to go operational | Central mapping of all highway servers, web domains, toll applications, cloud workloads, and field controllers |
| CERT-In Breach Reporting | Within 6 Hours of detection or notice | Immediate escalation of ransomware, unauthorized access, API leaks, or tolling outages to CERT-In |
| ICT System Log Retention | Minimum 180 Days immutable retention | Rolling storage of firewall, server, network access, and application logs inside Indian jurisdiction |
| Annual Security Audits | 282-Point Checklist by CERT-In Auditors | Annual vulnerability assessments, penetration testing (VAPT), network segmentation, and EDR validation |
Why Highway Cybersecurity Directly Affects Motorists and Fleet Operators
For daily highway drivers and commercial hauliers holding a Form 48 National Permit, highway IT security governs far more than backend office computers:
- Safeguarding Roadside ATMS & MLFF Gantries: With toll plazas transitioning toward barrierless Multi-Lane Free Flow (MLFF) gantries, roadside ANPR cameras, RFID readers, and fiber-optic cabinets act as internet-connected collection nodes. Mandatory network segmentation and Endpoint Detection and Response (EDR) stop roadside field cabinets from becoming entry points into national toll clearing networks.
- Protecting Vehicle Registration & Owner Contact Records: Earlier incidents involving historical bulk vehicle datasets highlighted how leaked plate-to-phone mappings fuel targeted fake e-challan SMS campaigns. Strict encryption, tighter database access control, and third-party vendor training directly cut the risk of new motorist data leaks.
- Preventing Fake Toll & E-Challan Spoofing: Maintaining accurate digital asset inventories within three months ensures unmonitored legacy subdomains or test APIs cannot be hijacked by phishing groups posing as Parivahan or IHMCL payment gateways.
echallan.parivahan.gov.in rather than clicking SMS links. Review our checklist on how to spot fake e-challan phishing texts and verify pending dues via the Official E-Challan Verification Guide.
Third-Party Contractors Brought Under Audit Scope
Because highway toll collection, variable message signboards, and cloud traffic dashboards rely heavily on private concessionaires and system integrators, the MoRTH directive extends mandatory cybersecurity training, strict role-based access rules, and VAPT testing obligations to third-party vendors working with NHAI and NHIDCL. Combined with a unified Security Operations Centre (SOC) tracking highway ICT health continuously, the framework brings India's national road grid in line with national critical-sector cyber standards.